Purple Team Lab · 2026

Operation
Silent SSH

Phishing → Credential Theft → SSH Account Takeover → Forensic Detection.
Every step mapped to MITRE ATT&CK. Every step caught.

↗ GitHub Repo Explore the Attack
9
MITRE Techniques
4
Log Sources
<5m
Full Attack Duration
0
Malware Used
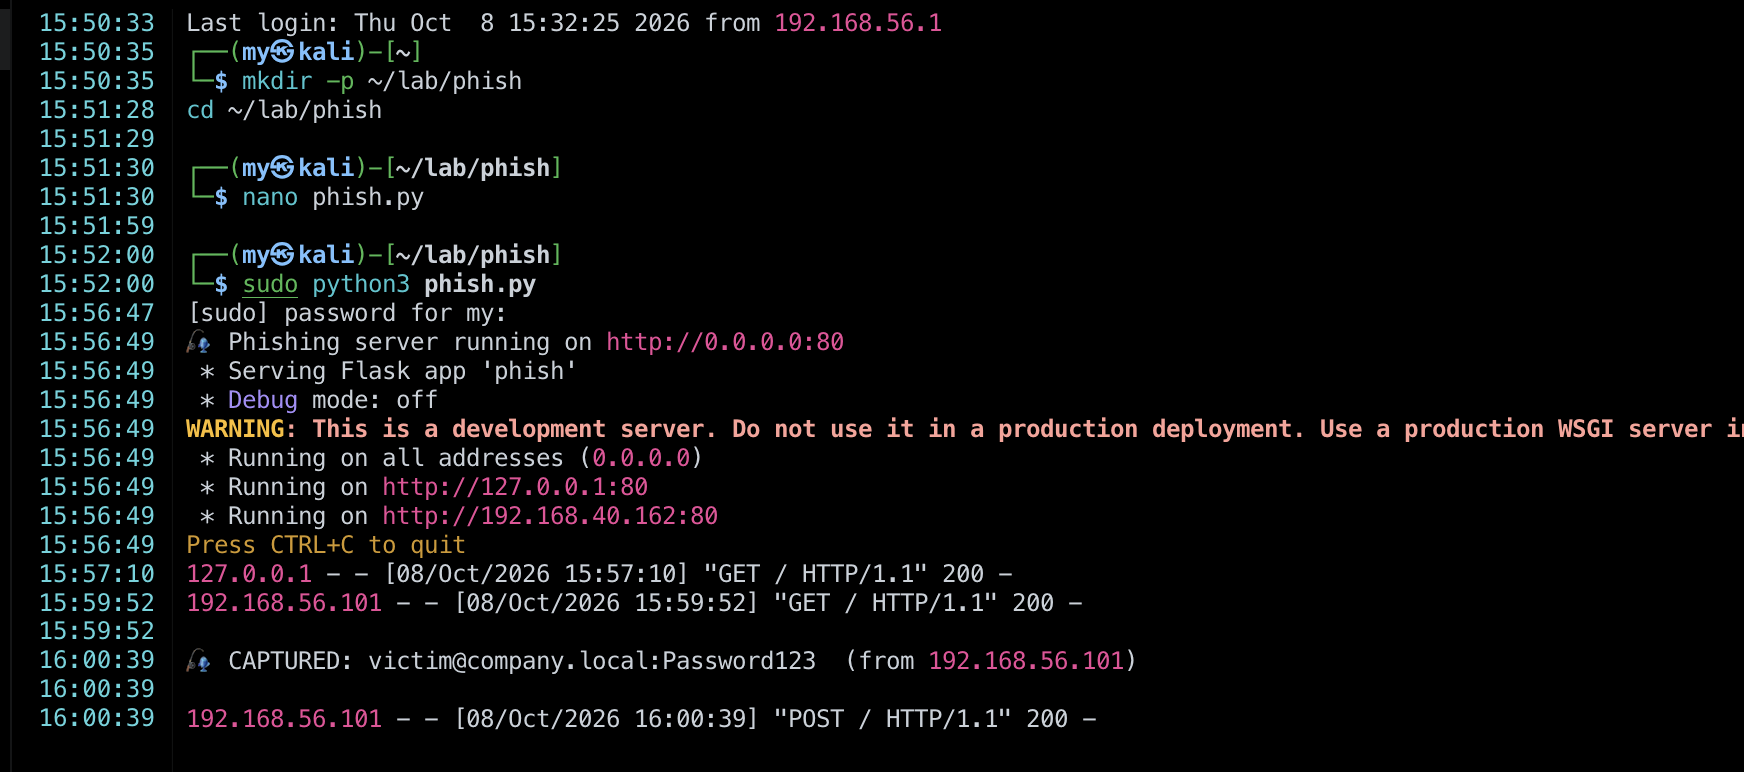
kali@attacker:~/lab/phish — attack timeline
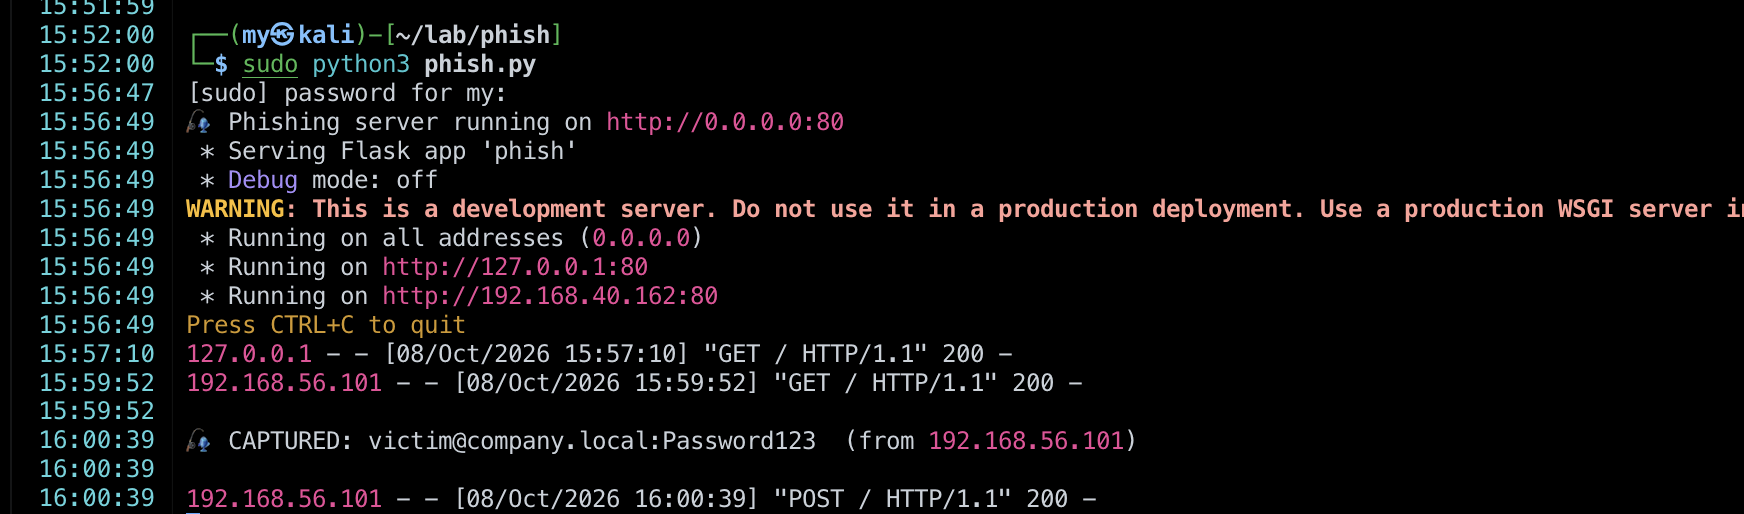
[15:57:10] $ sudo python3 phish.py
🎣 Phishing server running on http://0.0.0.0:80
* Serving Flask app 'phish' · Debug mode: off
 
[15:59:52] 192.168.56.101 — "GET / HTTP/1.1" 200 —
[16:00:39] 🔴 CAPTURED: victim@company.local:Password123 (from 192.168.56.101)
[16:00:39] 192.168.56.101 — "POST / HTTP/1.1" 200 —
 
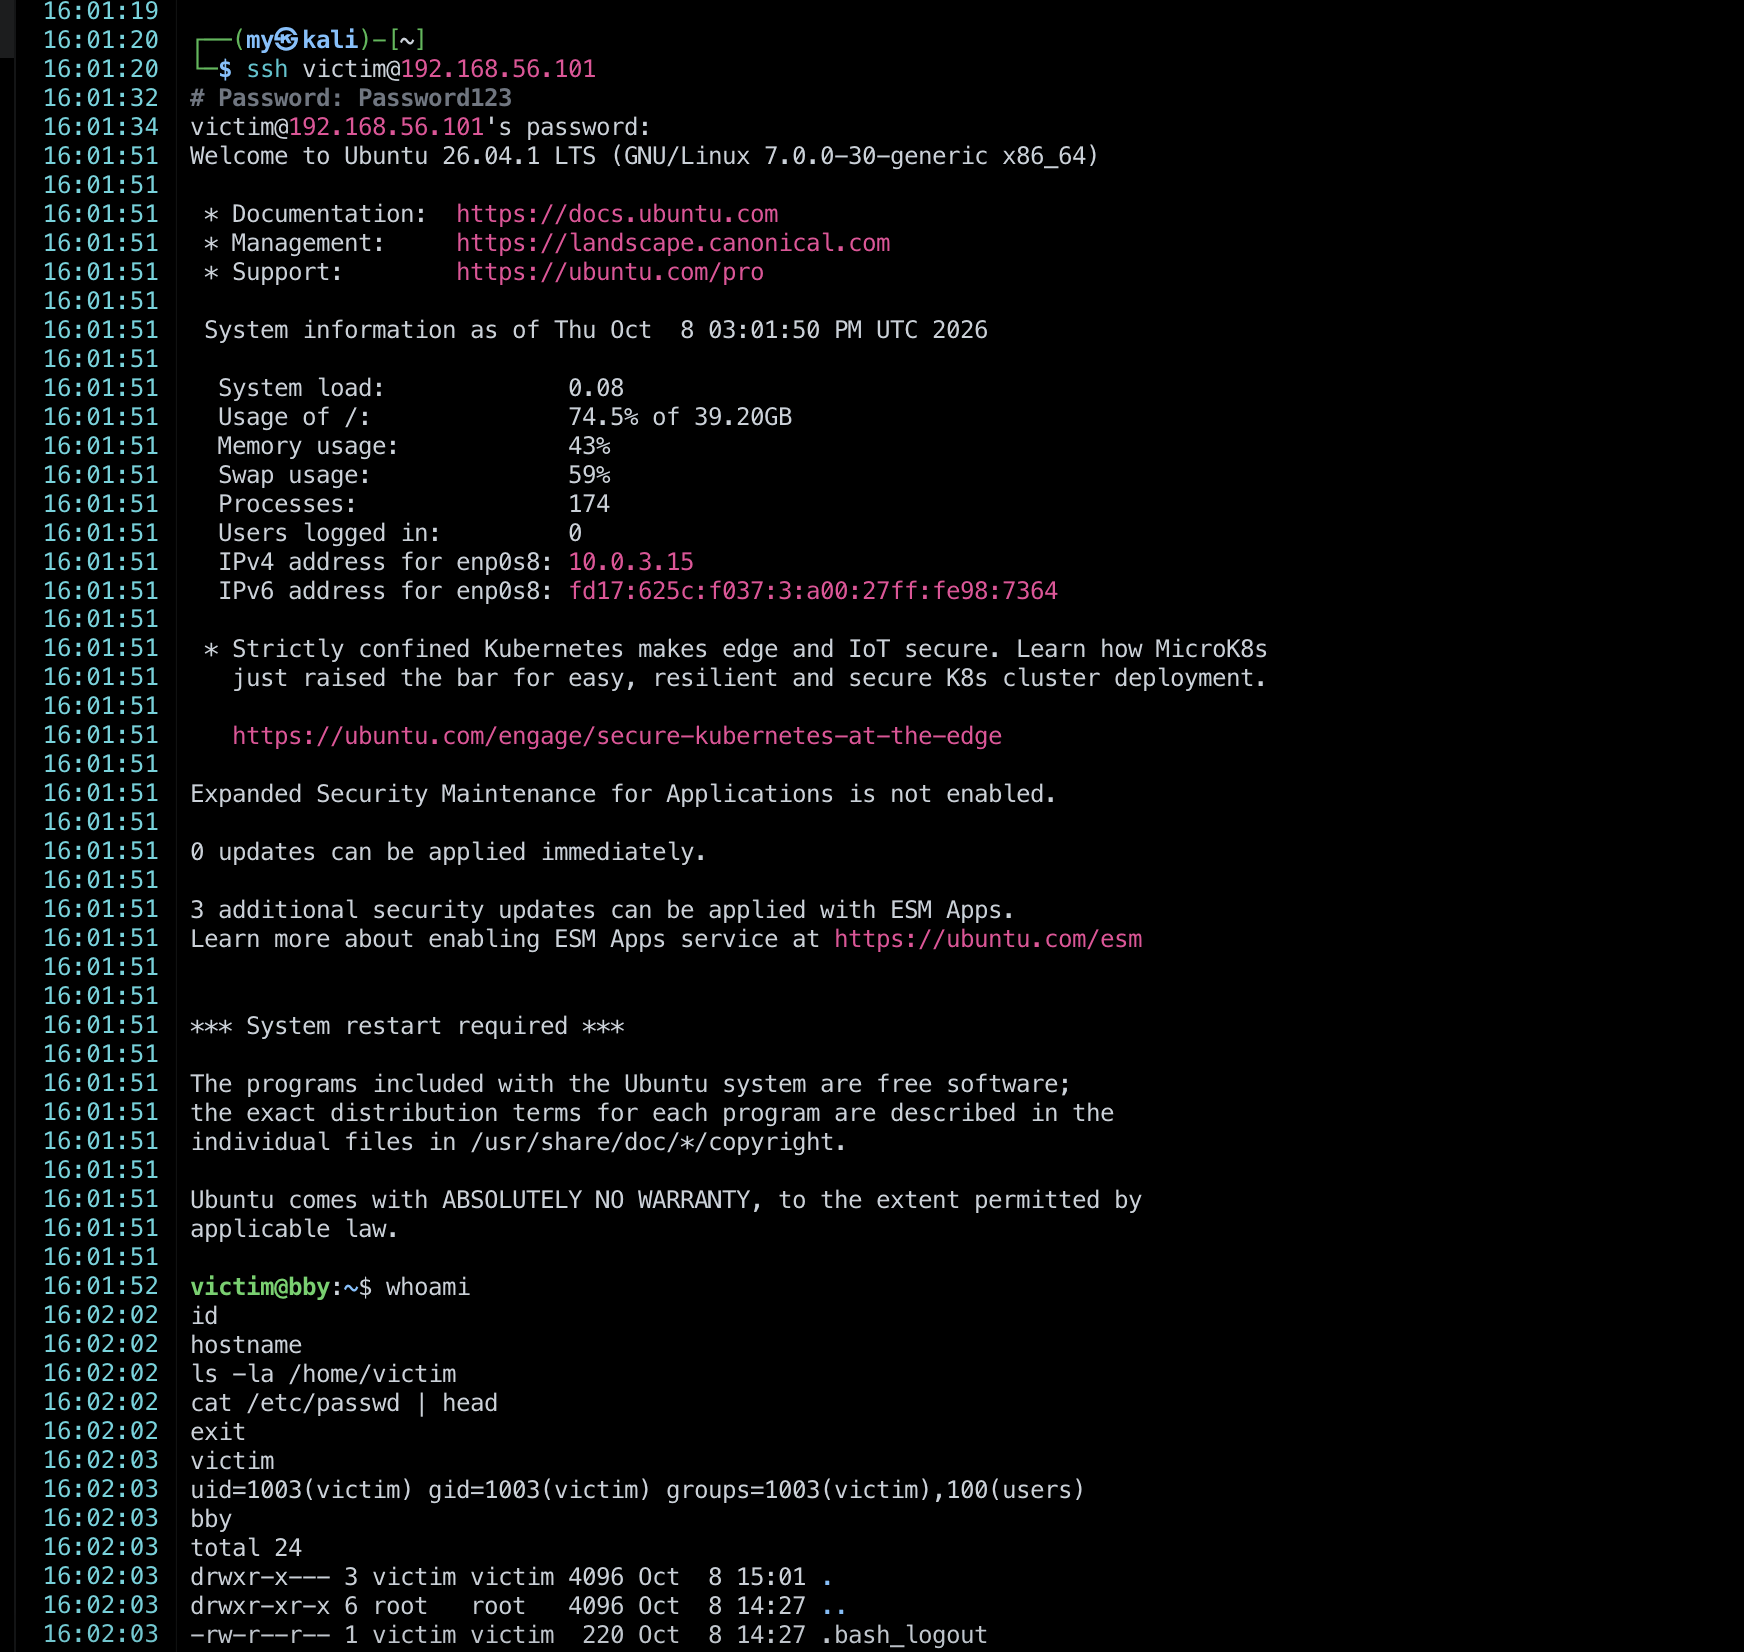
[16:01:49] $ ssh victim@192.168.56.101
victim@192.168.56.101's password: ████████████
Welcome to Ubuntu 26.04.1 LTS
 
victim@bby:~$ whoami && id && hostname
victim
uid=1003(victim) gid=1003(victim) groups=1003(victim),100(users)
bby
 
[16:02:04] Session closed. .bash_history written. Evidence preserved.

How the Attack Unfolded

A full identity-based attack executed with no malware — just a phishing page and an SSH client.

01
Reconnaissance
Target Identification
Identified Ubuntu Server at 192.168.56.101 with SSH port 22 open. Confirmed password authentication enabled.
T1595 — Active Scanning
02
Initial Access
Flask Phishing Server
Deployed a pixel-perfect fake CompanyCorp SSO login page on Kali port 80 using Python Flask. Victim browsed to http://192.168.56.10/.
T1566.002 — Spearphishing Link
03
Credential Access
Credentials Captured
Victim submitted credentials via HTTP POST. Server logged: [16:00:39] IP=192.168.56.101 USER=victim@company.local PASS=Password123
T1056.003 — Web Portal Capture
04
Lateral Movement
SSH Account Takeover
Used stolen credentials to SSH into the victim machine. Accepted password for victim from 192.168.56.10 — full shell access achieved.
T1021.004 — Remote Services: SSH
05
Discovery
Post-Exploitation Recon
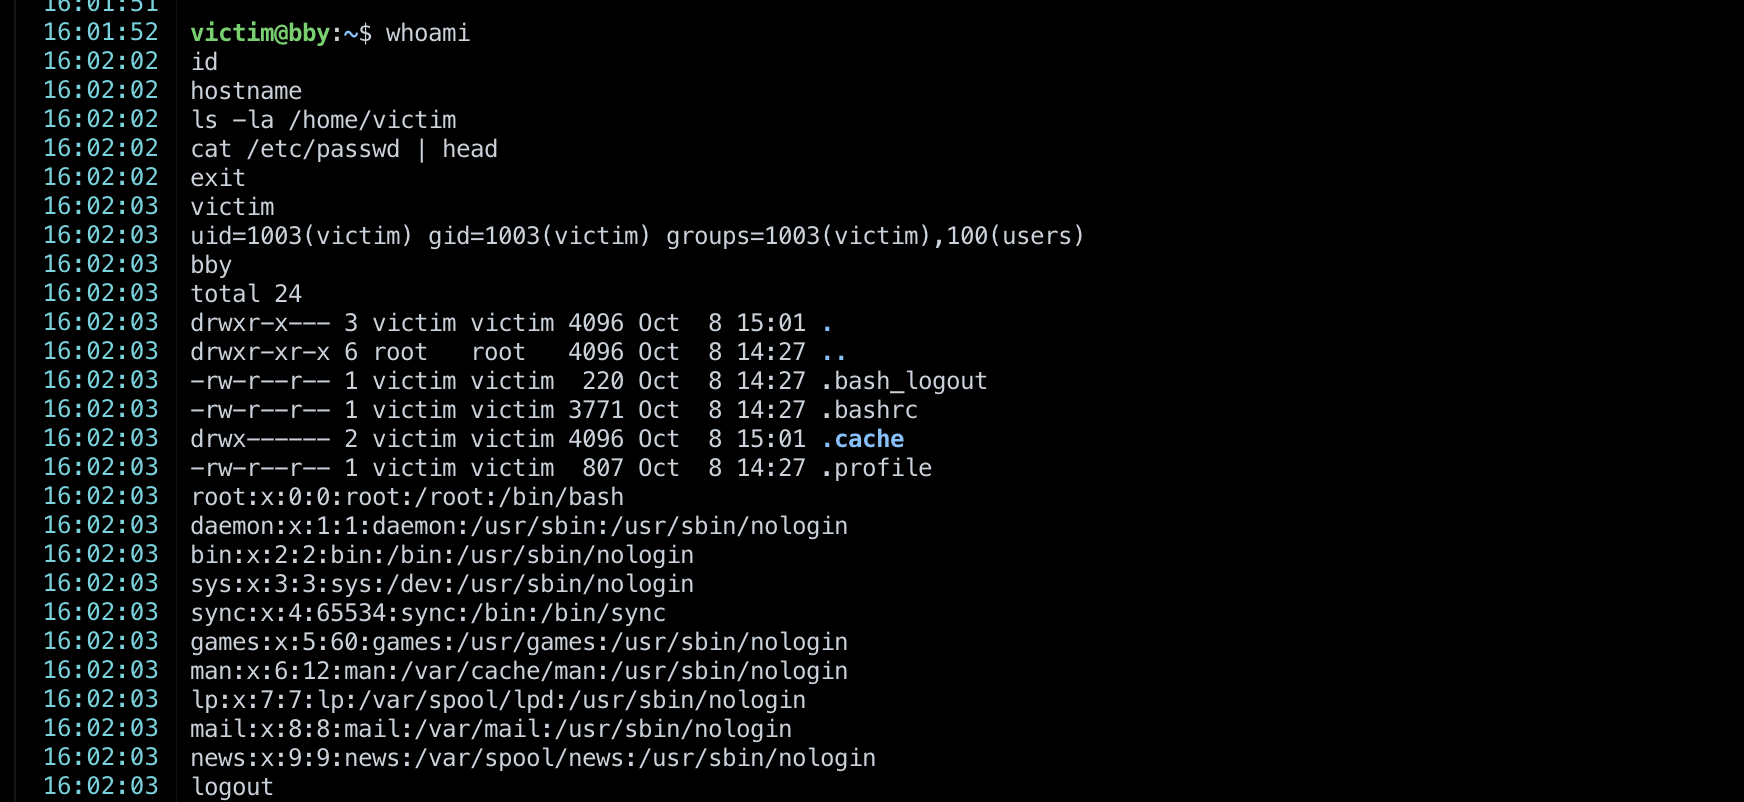
Ran whoami · id · hostname · ls -la /home/victim · cat /etc/passwd — standard attacker discovery pattern, fully logged by auditd.
T1033 · T1087.001 · T1005
✓
Detection
Every Step Caught
auth.log, auditd, and systemd-logind all fired. Session ID ses=5 correlates events across all 4 log sources. .bash_history preserved attacker commands.
MFA would have stopped this entirely

Live Lab Screenshots

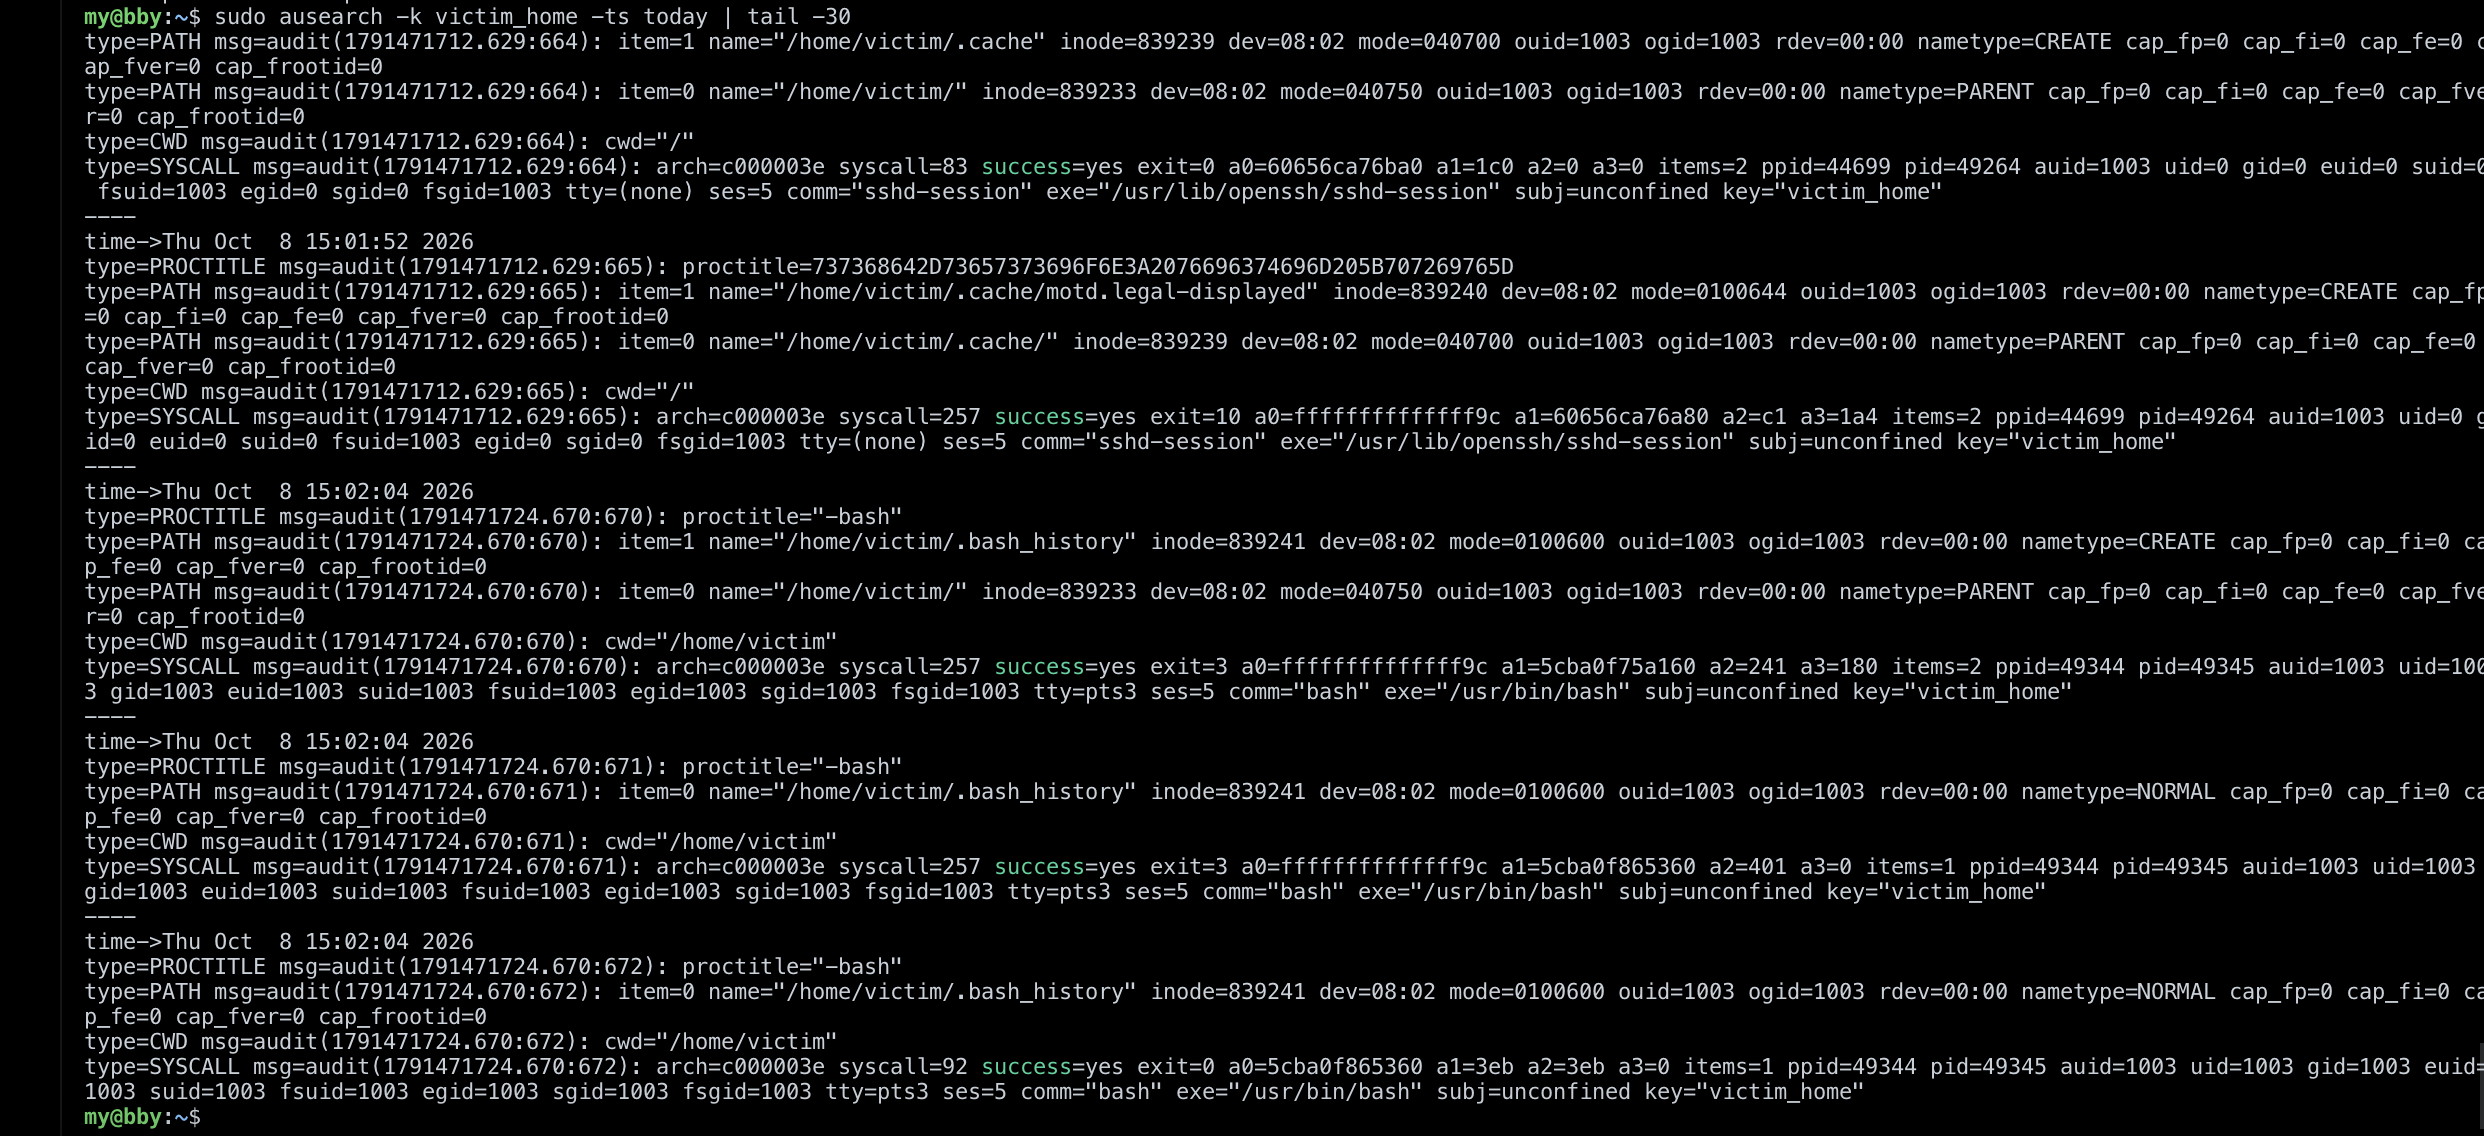
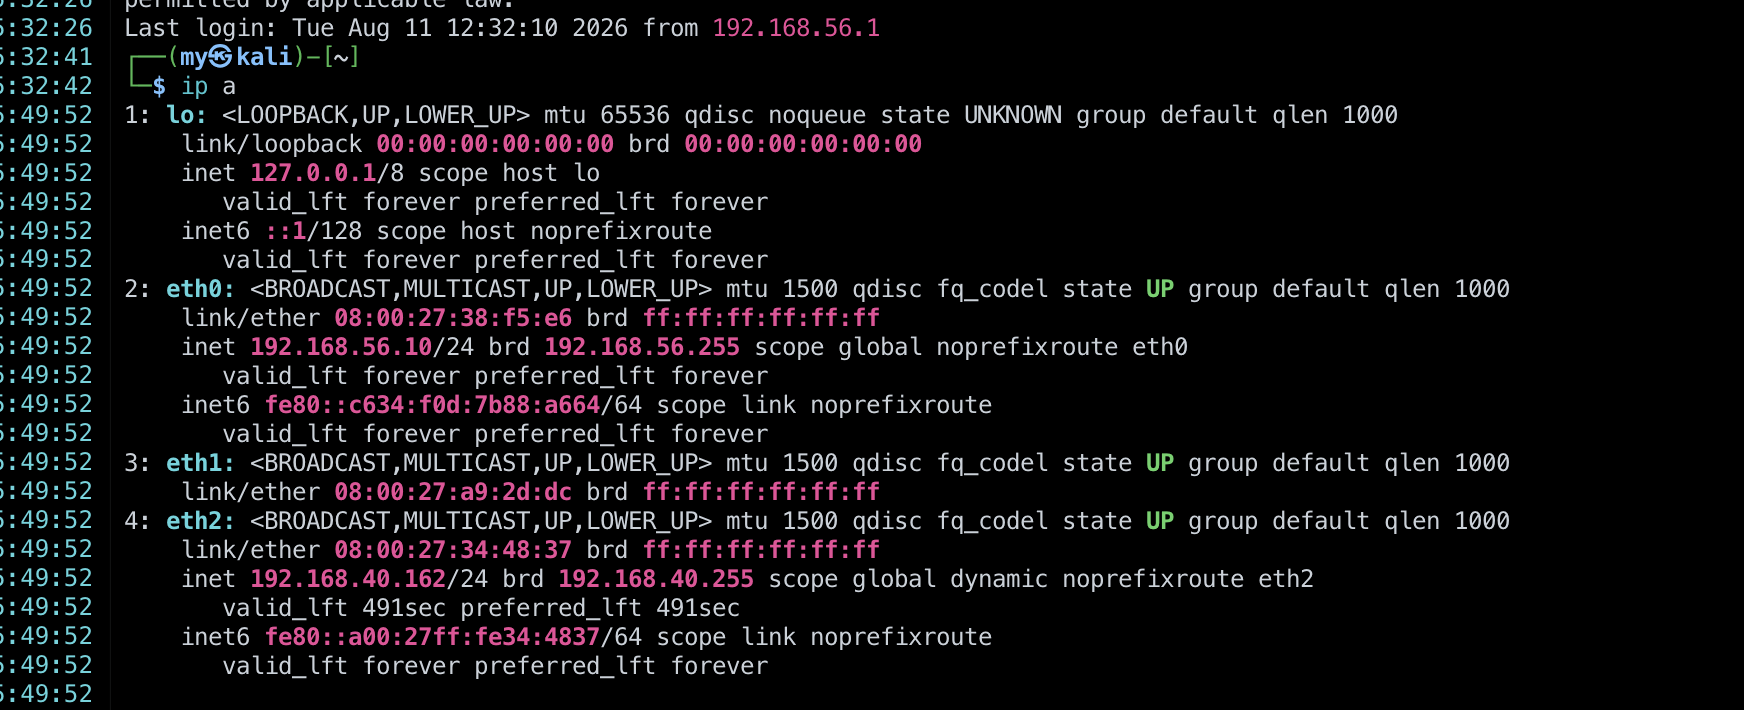
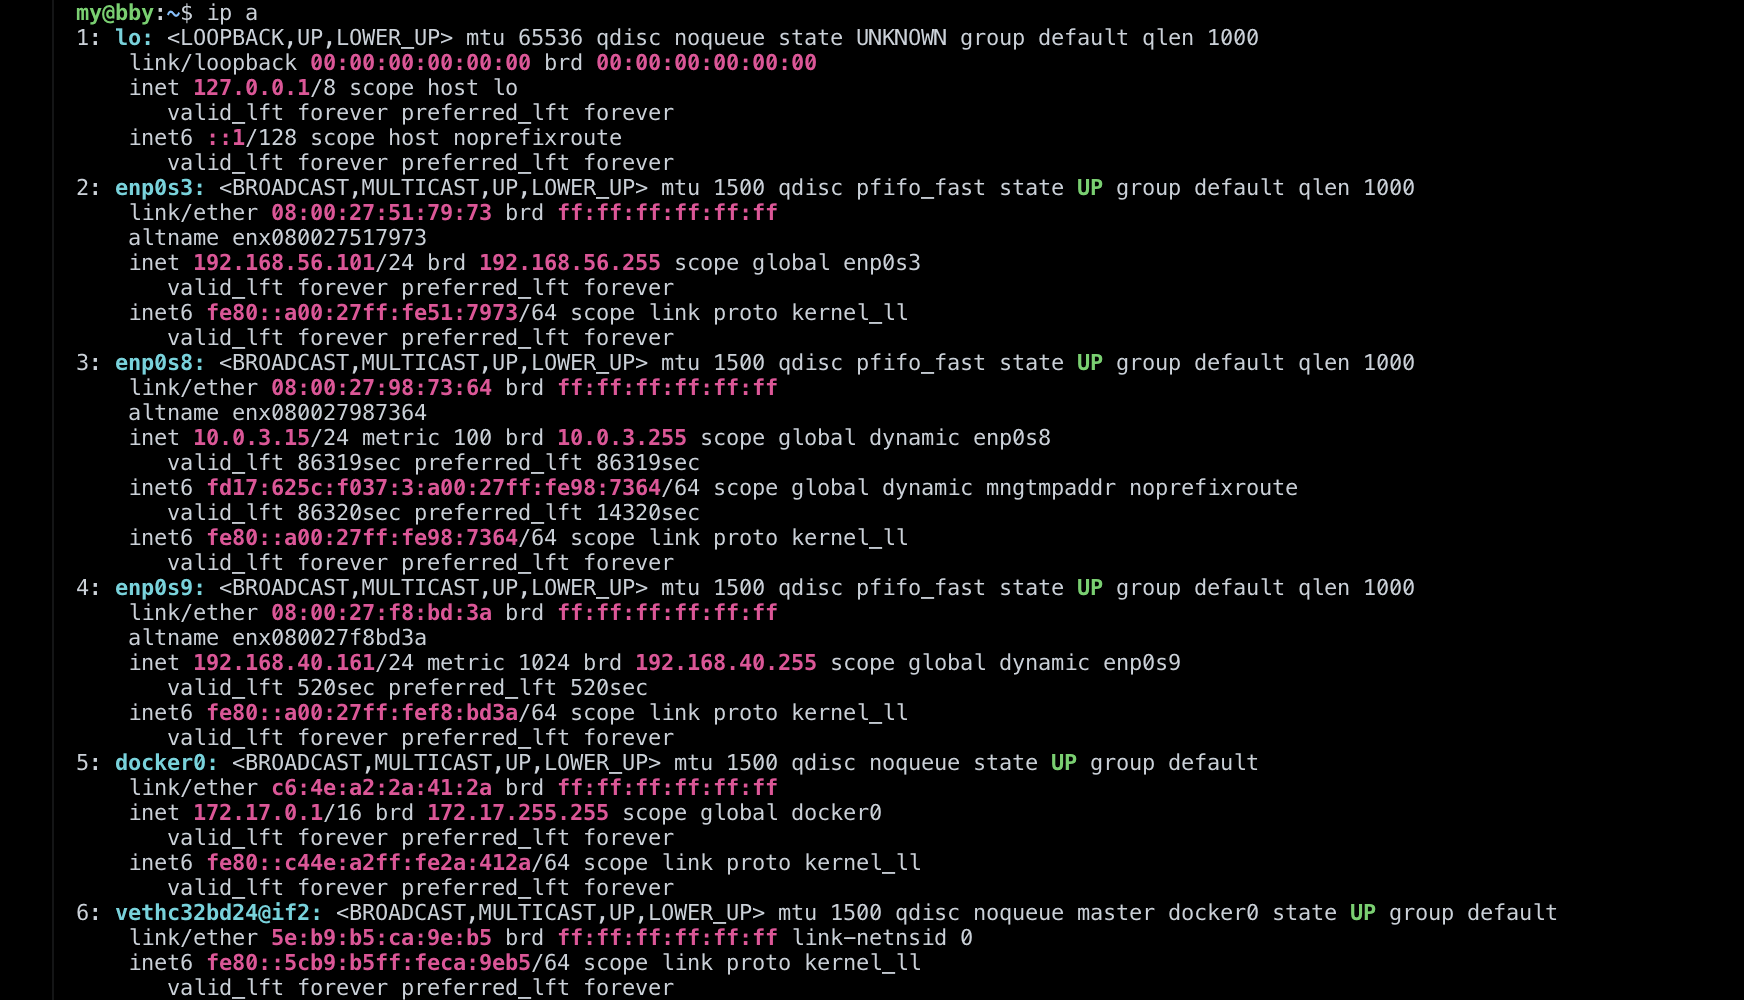
Real captures from the lab run — Kali attacker side and Ubuntu victim side.
Attack Timeline

Complete sequence of events from setup to detection — under 5 minutes.

14:27 UTC
victim account created on Ubuntu
sudo adduser victim · uid=1003
14:46 UTC
auditd watch rules configured
auditctl -w /home/victim -p wa -k victim_home
15:57:10 UTC
Phishing server started on Kali:80
Flask serving fake CompanyCorp SSO page
15:59:52 UTC
Victim visits phishing page
GET / HTTP/1.1 from 192.168.56.101
16:00:39 UTC
🔴 Credentials captured
victim@company.local : Password123 → creds.txt
16:01:49 UTC
🔴 SSH login — account takeover
Accepted password for victim from 192.168.56.10 · ses=5
16:01:52 UTC
auditd logs session init
comm="sshd-session" auid=1003 ses=5 key="victim_home"
16:02:02–04 UTC
Post-exploitation commands executed
whoami · id · hostname · ls -la · cat /etc/passwd
16:02:04 UTC
✅ Attacker exits — .bash_history written
auditd captures bash history write · full forensic record preserved

ATT&CK Technique Coverage

9 techniques across 6 tactics. Load the layer in ATT&CK Navigator to see the full map.

Open ATT&CK Navigator ↗
T1595
Reconnaissance
Active Scanning
T1583.005
Resource Development
Acquire Infrastructure: Server
T1566.002
Initial Access
Phishing: Spearphishing Link
T1056.003
Credential Access
Input Capture: Web Portal
T1078.003
Initial Access
Valid Accounts: Local
T1021.004
Lateral Movement
Remote Services: SSH
T1033
Discovery
System Owner/User Discovery
T1087.001
Discovery
Account Discovery: Local
T1005
Collection
Data from Local System

Detection Across 4 Log Sources

Every single attacker action was logged. Session ID ses=5 correlates events across all sources.

📋
auth.log
Captured the exact moment of SSH login with source IP, username, port, and timestamp.
Accepted password for victim
from 192.168.56.10 port 40850 ssh2
🔍
auditd
Watched /home/victim for writes. Caught both sshd session init and .bash_history write on exit.
auid=1003 ses=5 key="victim_home"
comm="bash" exe="/usr/bin/bash"
⚡
systemd-logind
Tracked session lifecycle — creation and termination with session ID for cross-correlation.
New session '5' of user 'victim'
class 'user' type 'tty'
📜
.bash_history
Attacker forgot to clear history. Full command sequence recovered — forensic gold.
whoami · id · hostname
ls -la /home/victim
cat /etc/passwd | head